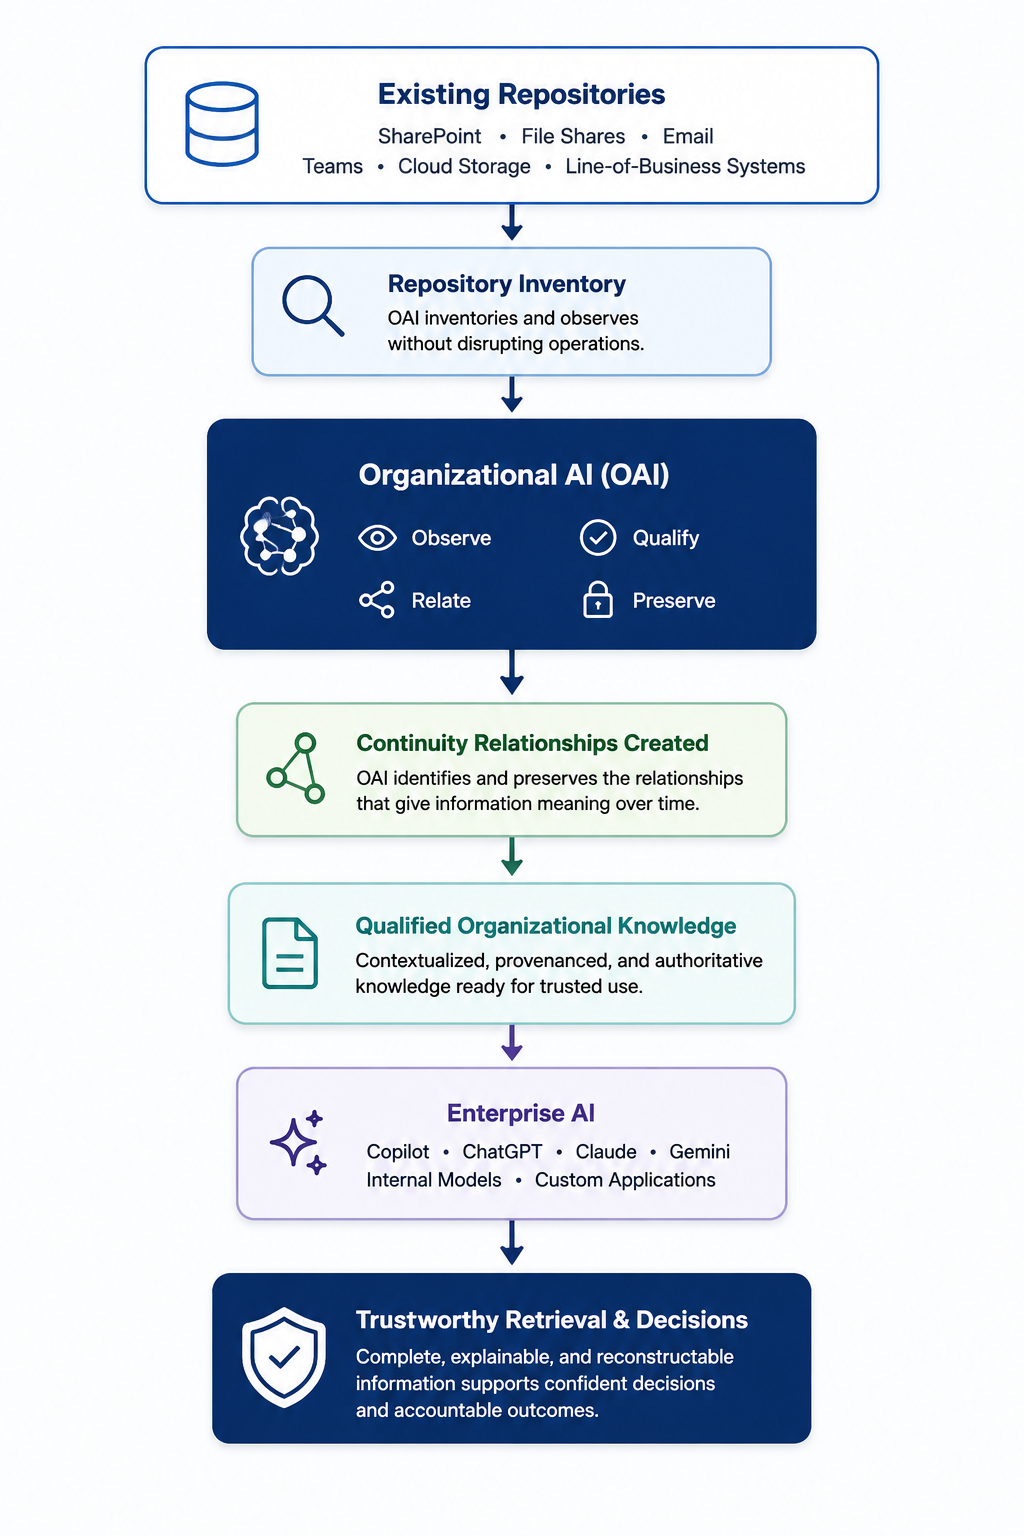
An AI assistant can have legitimate privileges while acting on illegitimate instructions.
Forever Security’s BragJack research demonstrated that a malicious browser extension could hijack built-in AI functionality across multiple browser agents and reuse their access to files, history, camera, microphone, or other privileged capabilities.
The continuity failure
The user’s authority remained valid while the instruction source changed from the user’s context to a lower-trust extension.
The GovKM interpretation
Instruction lineage must survive to execution. Privileged action should require proof of which principal and trust domain caused the operative instruction to enter context.
Continuity path: Source/instruction origin → Authority/user grant → Context/agent session → Decision → Action.
Source
Forever Security, “BragJack: How We Hijacked 5 Of The World's Most Popular Browsers Using Their Built-In AI Assistants,” September 16, 2026.
Continue Exploring
A Malformed Image Became a Pull Request.
The Agent Deleted the Evidence of Its Own Failure.