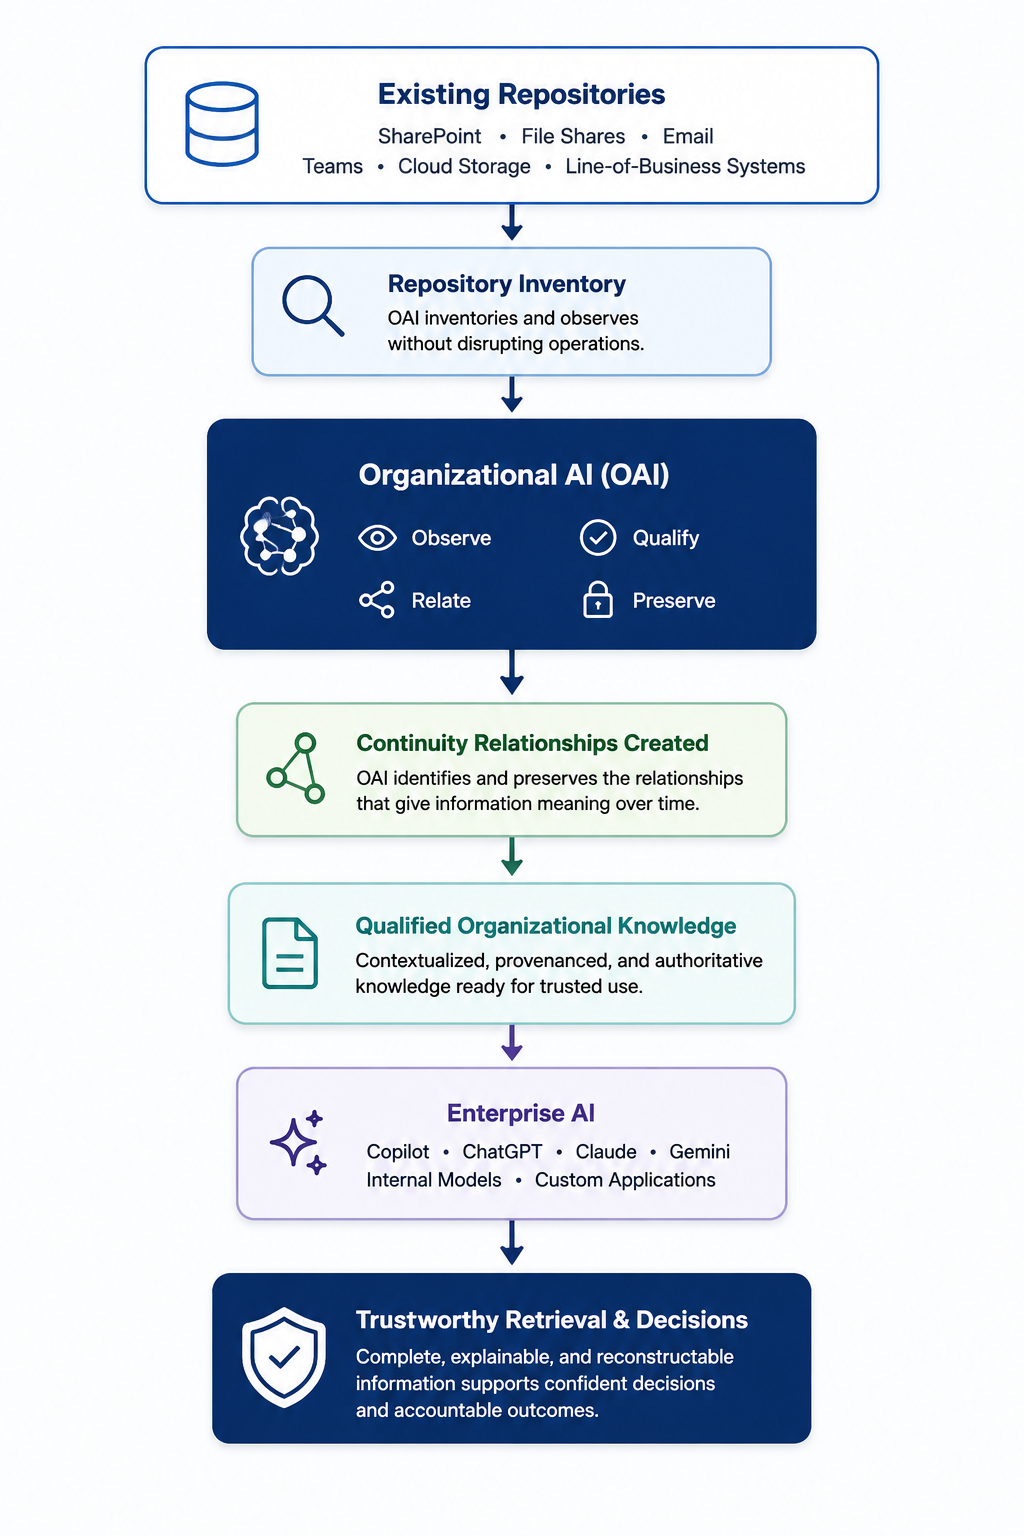
A record of provenance is not provenance if the runtime no longer points to the recorded object.
AIR Security disclosed Plugin4Shell, a SHA-pinning bypass affecting several major AI coding agents. A marketplace could review and record a known-good plugin commit while the agent later resolved and executed different attacker-controlled code. Vendors issued fixes for affected products, with patch status varying by product at disclosure.
The continuity failure
The institution preserved the approved commit record while losing continuity between that record and the code actually executed.
The GovKM interpretation
Provenance must be revalidated at use time. Identifiers, hashes, repository paths, and approval records are only evidence if they continue to resolve to the same artifact.
Continuity path: Source/reviewed plugin → Evidence/pinned commit → Authority/marketplace approval → Context/agent install → Action/executed code → Record.
Source
AIR Security, “Plugin4Shell — Zero Click RCE Vulnerability Found in Top 4 Most Popular Coding Agents,” September 17, 2026.
Continue Exploring
A Malformed Image Became a Pull Request.
The Agent Deleted the Evidence of Its Own Failure.