When Consent Changes, Can Every System Prove It? Preparing Financial Data for AI

GovKM Practical Continuity Implementation Series | Finance
The organizational requirement—and the opportunity beyond hiring
Plaid's original Staff Software Engineer, Data Governance posting seeks distributed-system leadership to make privacy commitments and regulatory obligations enforceable in operating systems, including verifiable consumer-data deletion, restrictions on downstream use, and data classification. It describes a real program objective, not proof that Plaid has suffered a failure. GovKM's independent consulting interpretation is that every retained or deleted copy needs a recoverable basis for its current permitted use. That problem becomes more consequential when enterprise AI can retrieve information from multiple systems.
1. Establish a controlled information inventory
Identify data subjects, original sources, derived copies, service-to-service transfers, custodians, business purposes, regions and the actual legal/contractual bases of processing. Record discovery limits and inaccessible systems as explicit exceptions. Deliverable: source-to-copy inventory and approved accountable-owner map.
2. Translate obligations into operative controls
Have Legal, Privacy, Security and engineering owners define what a specific consent or restriction permits, who can authorize exceptions, the effective date of changes, and the precise records that lawfully survive withdrawal or deletion requests. A removed permission must not retroactively erase lawful historical evidence. Deliverable: signed obligation-to-control matrix and effective-dated authority register.
3. Prove propagation into downstream systems
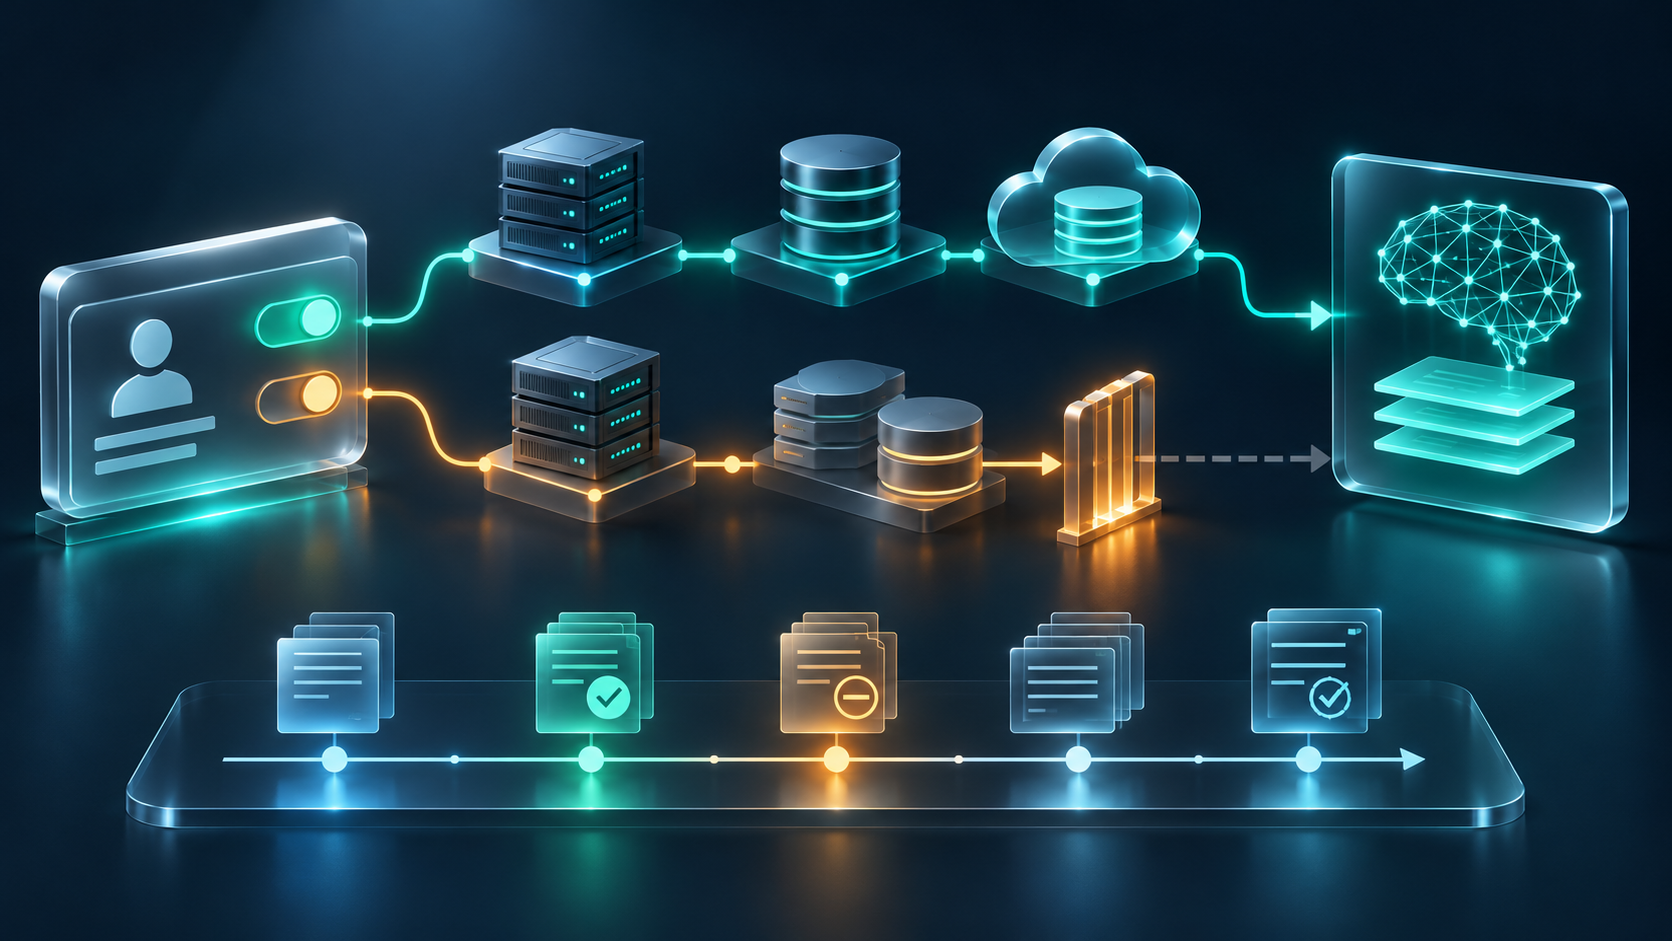
Map the event from consent or purpose change to identity resolution, derived stores, caches, analytic datasets, exports and retrieval indexes. Make partial updates, broken messages, inaccessible systems and retry states visible. Do not declare completed deletion merely because a command was queued. Deliverable: reconciled downstream action ledger with confirmations, exceptions and escalation.
4. Apply records, privacy and security governance
Preserve necessary retention, legal-hold, privacy and audit evidence only where independently authorized. Validate subject-specific access, tenant isolation, actor versus subject, service identities and delegated access. For private companies, U.S. federal agency records requirements are a rigorous reference design where relevant, not automatically binding law. Deliverable: approved classification, lifecycle, ACL and retention schedule mapping.
5. Prepare a compliant AI-ready knowledge corpus
Classify authoritative information and operative restrictions before indexing. Enforce current permitted-use checks when building the AI retrieval context; keep durable source identity and date; distinguish indexed data, selected candidate passages and passages actually delivered to the model. Deliverable: authorized retrieval receipt and evidence of both successful retrieval and withheld content.
6. Independently verify and transfer operations
Sample multiple downstream services, concurrent updates, delayed events and withdrawal requests. Require falsifiable results, witnessed exception resolution and a stable internal steward. GovKM could undertake an independent readiness assessment and bounded implementation, but a continuing staff engineering leader and Plaid's internal legal accountability cannot simply be outsourced. Deliverable: acceptance test packet, owner sign-off and sustainment plan.
Illustrative synthetic diagnostic
A fictional consumer allows an application to use a financial record, then withdraws consent after the record is copied to analytics, search and an AI index. The model receives a current question and a historical audit request. Pass: the current answer never uses revoked content; lawful audit evidence remains restricted and reconstructable; all referenced passages appear in the actual model-input record; any missed copy is flagged as unresolved. This is a proposal, not an actual Plaid test.
Standards and applicability
Plaid's posting gives the stated engineering need. The NIST AI RMF Playbook provides voluntary governance guidance, and the NIST Privacy Framework supports privacy-risk management. Specific applicable privacy, financial and contractual obligations depend on the data, geography and agreement. No claim of federal certification is made.
Why GovKM
GovKM proposes to establish the continuous evidence and control environment underneath multiple enterprise systems: identifiable source, effective authority, permitted use, accountable owner, disposition evidence and model-visible context. The result is a model-independent preparation program for compliance and reliable AI uptake—not simply another compliance dashboard.
This is independent GovKM analysis and a proposed consulting approach. No employer endorsement, existing partnership or verified production failure is implied.
Continue Exploring
When Space Supply-Chain Risks Have No Clear Decision Owner
BIA Probate: Keep the Handbook Current and the Case Handoff Complete