When Space Supply-Chain Risks Have No Clear Decision Owner
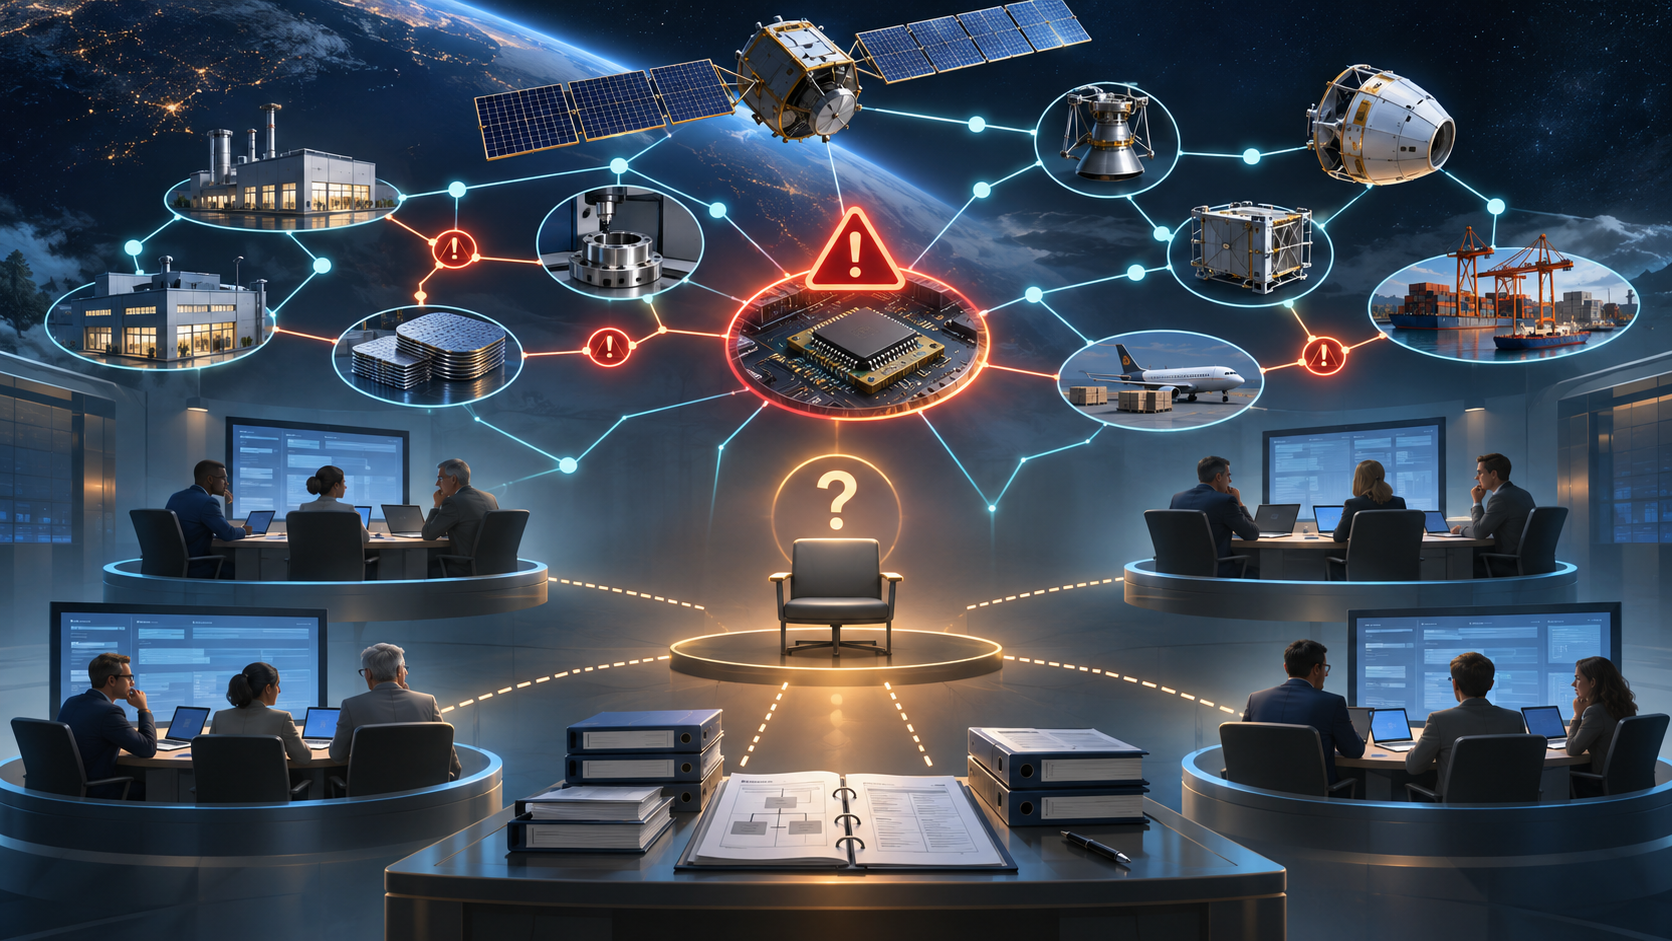

A risk can be known without anyone having clear authority to resolve it.
Recognizing a problem does not establish which evidence governs it, who can approve a response, or whether a later decision reflects changed circumstances. Without those connections, a record can accurately describe the risk while leaving its treatment and accountability uncertain.
What GAO found
In its November 17, 2026 report, Space Supply Chains: Additional DOD Actions Could Strengthen Its Enterprise Approach for Managing Risks, the Government Accountability Office examined risks affecting the national security space portfolio. DOD's expanding satellite constellations depend on industrial capacity distributed across suppliers and government organizations.
GAO found that an April 2026 memorandum for an enterprise risk-management service did not identify a lead agency or official or clearly define responsibilities. Guidance issued by Space Systems Command could not be enforced among participants outside the Space Force, including the National Reconnaissance Office. The report also documented supply-chain-related program delays. GAO recommended formal interagency agreements, clear leadership responsibilities and implementation guidance. DOD concurred, and all three recommendations remained open at review.
GAO did not conclude that every related decision was unsound, nor attribute the deficiencies to AI. The documented problem is the absence of a fully coordinated, authoritative enterprise risk-management approach.
The continuity problem
Consider a critical supplier whose manufacturing capacity becomes insufficient. One participant identifies the risk. Another maintains acquisition requirements. A third controls a potential mitigation. Each may possess accurate information without an agreed enterprise decision owner.
Which assessment governs? Who can approve mitigation? What happens when conditions change? Can successors reconstruct the decision and its evidence? A conventional risk register may show concern without preserving the authority, dependencies, applicable versions, decisions and subsequent actions needed to answer those questions.
What a governed solution requires
Federal agencies operate under existing documentation and internal-control obligations. 44 U.S.C. § 3101 requires adequate and proper documentation of agency functions, policies, decisions, procedures and essential transactions. GAO's 2025 Standards for Internal Control in the Federal Government, effective beginning in fiscal year 2026, establishes internal-control standards relevant to responsibilities, delegated authority, risks and information. These authorities do not prescribe GovKM or OrgAI; specific agency, records, access and security obligations must be assessed separately.
- Establish governing authority. Formally designate risk owners, decision rights and interagency agreements. Distinguish the information contributor from the official empowered to approve a response.
- Preserve authoritative evidence. Identify systems of record and retain the source, version, applicability period, responsible custodian and access constraints for each material assessment.
- Connect changes to reassessment. Changed supplier capacity, requirements or assumptions should initiate documented consideration of affected decisions and mitigations without silently overriding approved action.
- Record decisions and follow-through. Connect approvals and mitigation to their governing evidence, responsible offices, applicable records schedules and security controls.
- Test reconstructability. Verify that authorized reviewers can follow a risk from evidence through decision, action and subsequent review, documenting exceptions and corrective measures.
The objective is not another repository of risk documents. It is an environment where officials can determine what information is operative, who has authority, and what must be reconsidered when circumstances change. Compliance claims require mapped requirements, implemented controls and verification evidence, not design assertions.
Where OrgAI contributes
GovKM proposes OrgAI as a continuity-management capability supporting such an environment. At the publicly described functional level, OrgAI would help maintain governed relationships among sources, authority, decisions, actions and later changes, and identify missing, conflicting or superseded support for authorized review.
OrgAI would not independently establish government policy, delegate authority, approve mitigation or determine compliance. Responsible officials retain those functions. Deployment-specific capability claims require testing; this proposal is not evidence of an existing DOD deployment.
Why this matters beyond defense
Healthcare supplier management, financial third-party risk and retail distribution face comparable problems across organizational boundaries. Laws, agreements and security obligations differ, but the method of connecting evidence, authority, decisions and verification is reusable.
Related GovKM analysis addresses risk mitigation that fails to track new evidence and risk scores without enough decision context. The issue here is distinct: a multi-agency decision structure that has not clearly assigned governing authority.
A risk register should not merely demonstrate that a problem was recognized. Its records should enable the institution to show how that problem was governed, decided and addressed. GovKM helps organizations assess continuity gaps and prepare governed information environments for accountable operations and AI adoption. Contact GovKM to discuss an information-continuity assessment.
Continue Exploring
BIA Probate: Keep the Handbook Current and the Case Handoff Complete
BOP Death Reviews: Keep Facility Recommendations Visible Through Correction