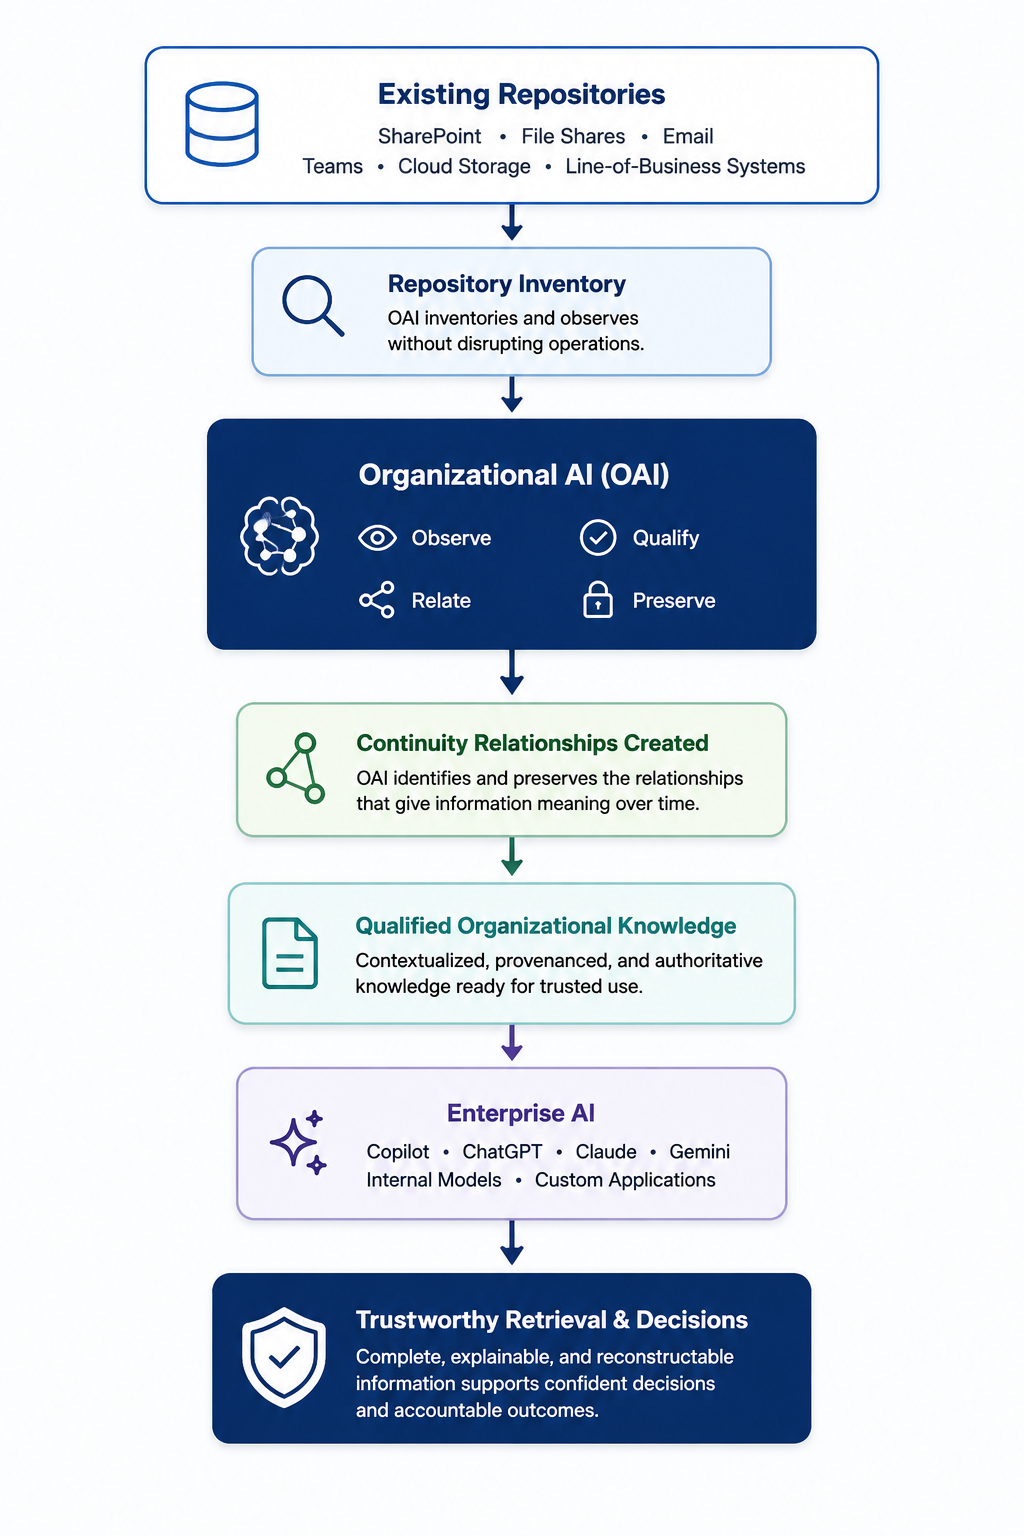
A control is not independent when the controlled environment can influence the boundary.
Accomplish AI disclosed two Codex sandbox escapes. One allowed patch tooling to widen write permissions; another allowed code in the untrusted context to recover a trust token from shared process memory and communicate with an unsandboxed parent process. OpenAI patched both issues before publication.
The continuity failure
The environment being constrained could affect the mechanism that translated policy into runtime permission.
The GovKM interpretation
Authority qualification should be causally separate from the actor whose action is being authorized. Governance that lives inside the same trust domain it controls can become self-referential rather than enforceable.
Continuity path: Authority/sandbox policy → Context/untrusted workload → Decision/permission → Action/host execution.
Source
Accomplish AI / Oren Yomtov, “Escaping the OpenAI Codex sandbox, twice,” September 15, 2026.
Continue Exploring
A Malformed Image Became a Pull Request.
The Agent Deleted the Evidence of Its Own Failure.