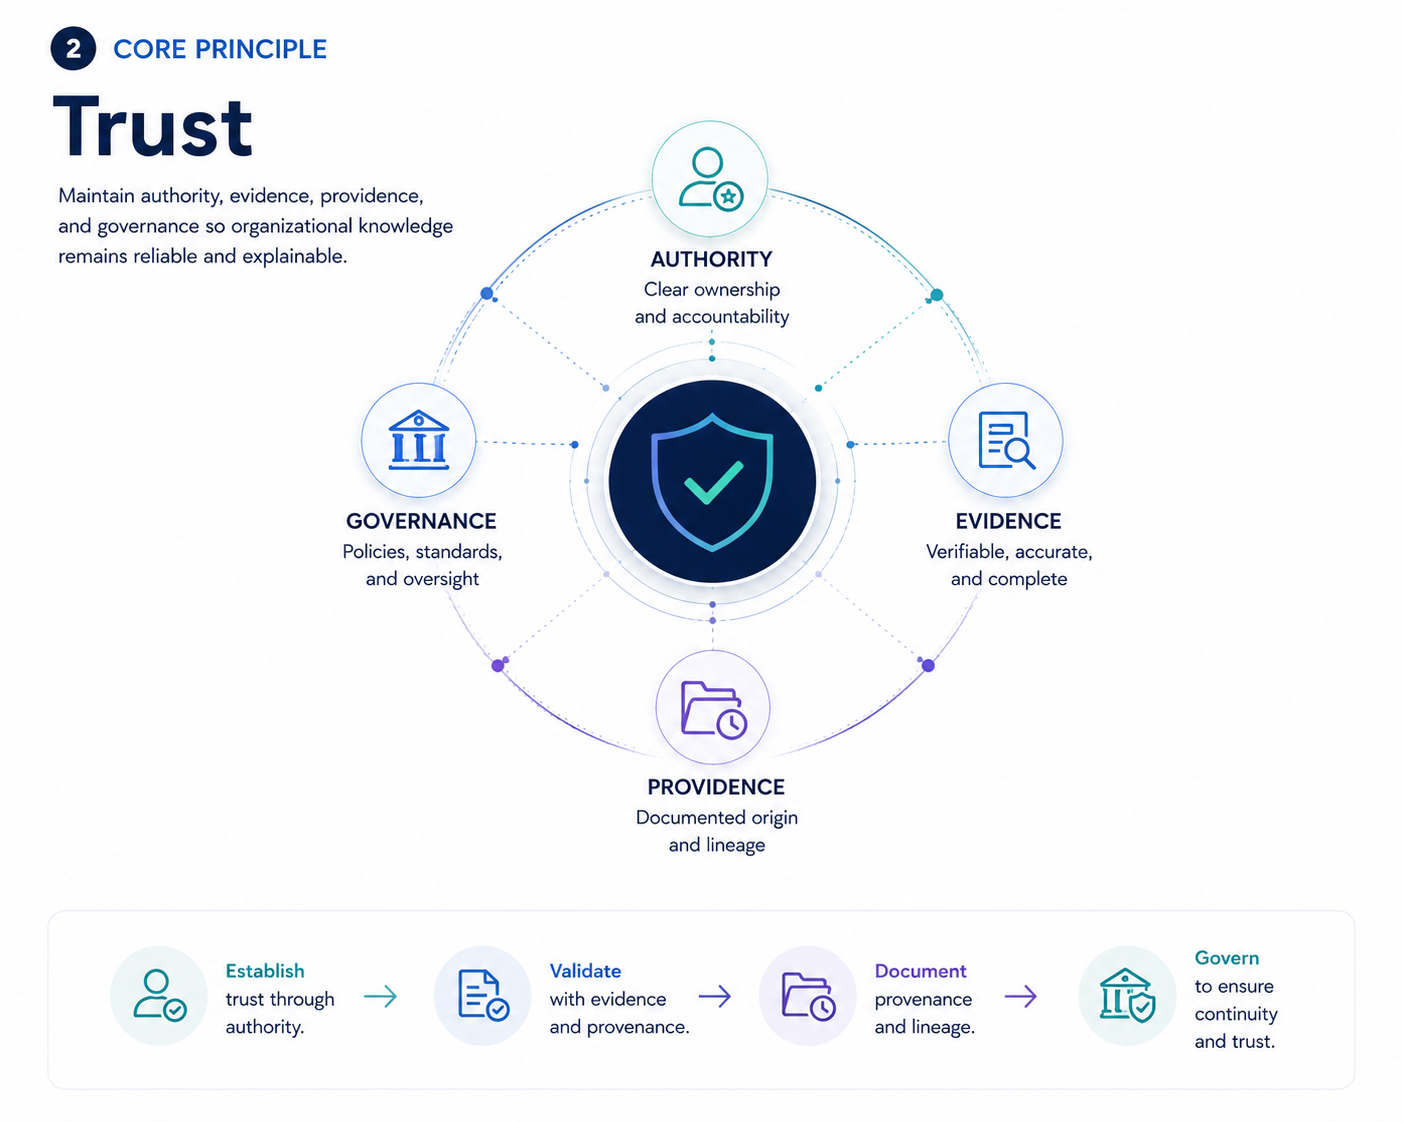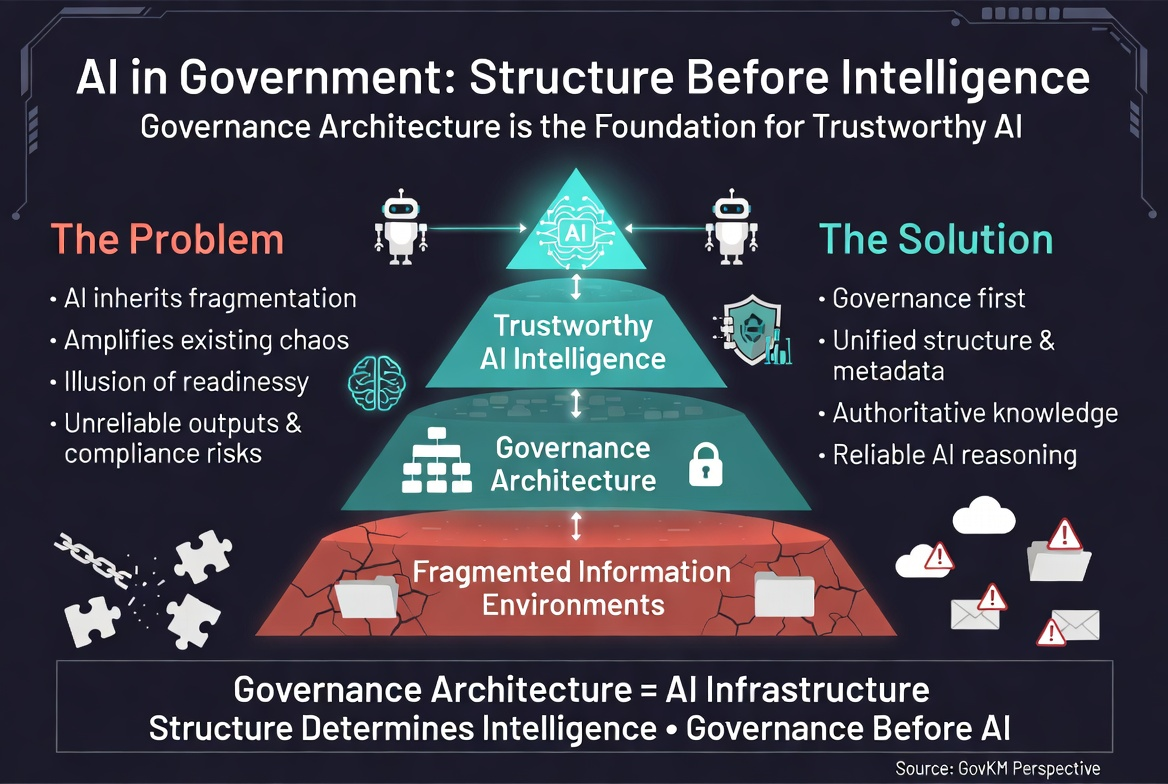

Permission to perform an action does not imply authority over every object that action can reach.
CVE-2026-77255 affected mcp-atlassian before version 0.22.0. The Jira update tool accepted attachment paths without adequately validating that they belonged to an authorized workspace. A caller could therefore induce the MCP server to read arbitrary local files and attach them to a Jira issue, using the server as a confused deputy.
The continuity failure
The system preserved authorization for the operation type—attach a file—but lost authorization for the specific source object.
The GovKM interpretation
Every consequential action needs at least three independently valid relationships: Authorized Action + Authorized Source Object + Authorized Destination. A valid operation does not confer source authority by default.
Continuity path: Source / workspace file → Authority / file-access scope → Context / Jira attachment action → Decision → Action / upload → Record / Jira issue.
Source
GitHub Security Advisory GHSA-2xj6-xx86-cwwc and OSV CVE-2026-77255, September 22, 2026.
Continue Exploring
COOP Keeps Government Operating. But What Keeps Its Information Continuous?
AI Needs Freedom. Freedom Needs a Constitution.