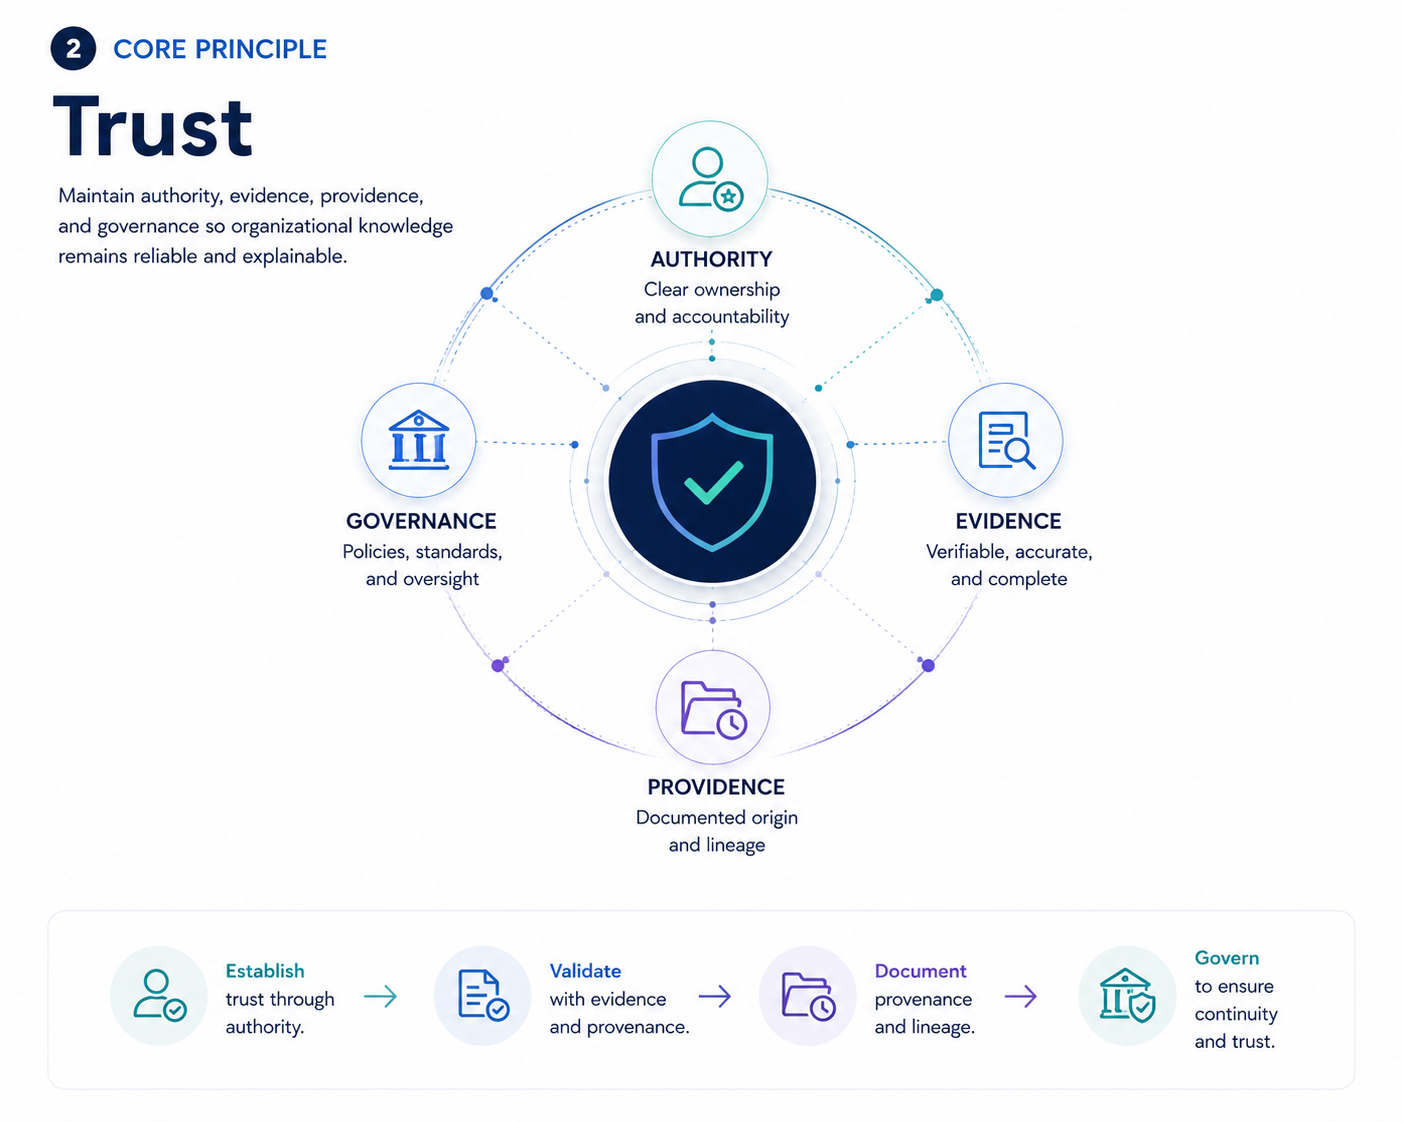

Evidence should not silently become command.
Zenity Labs’ SalesBleed research showed that malicious instructions embedded in public Salesforce Web-to-Lead records could later influence Agentforce when an employee asked an ordinary question about recent leads. The agent could then use existing permissions to access sensitive CRM data or send Slack messages through the agent identity. Salesforce remediated the reported paths before public disclosure.
The continuity failure
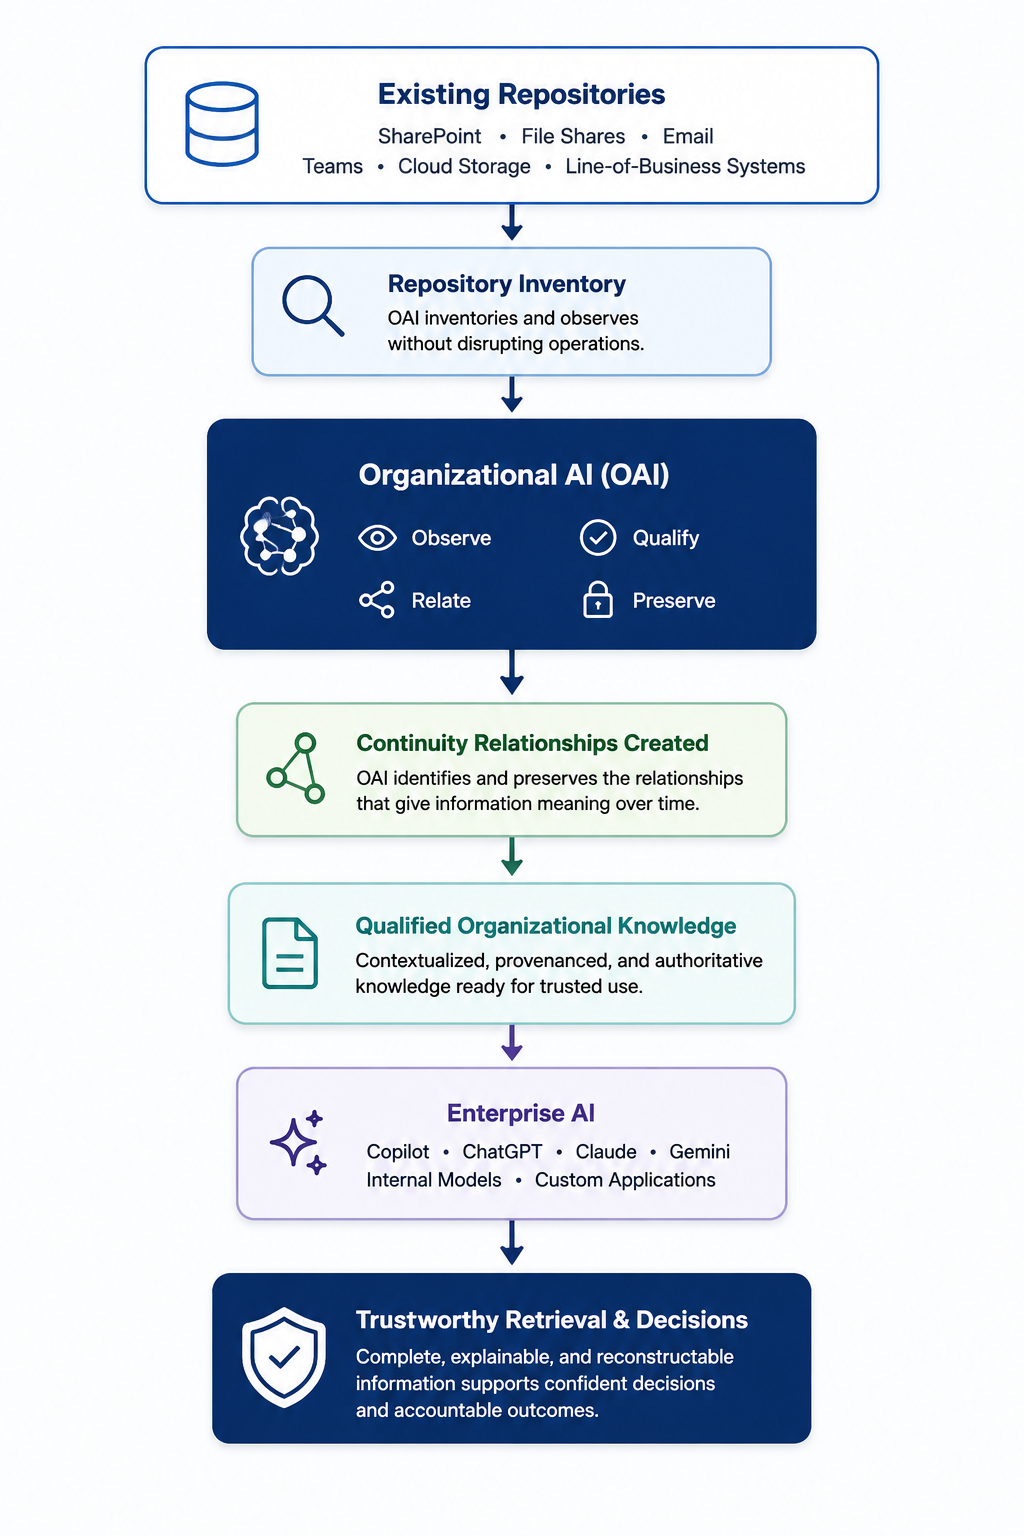
The system admitted the lead as business data, but the same object later acquired instruction authority inside a privileged agent context.
The GovKM interpretation
Every object entering AI context should retain its institutional role. A record may be evidence, content, policy, or instruction—but those roles are not interchangeable simply because the text contains imperative language.
Continuity path: Source / external lead → Record / CRM object → Context / agent session → Authority / instruction source → Decision → Action / CRM query or Slack message.
Source
Zenity Labs, “SalesBleed: Indirect Prompt Injection and 0-Click Data Exfiltration on Agentforce” and “SalesBleed: Hijacking Agentforce in Slack for Anonymous Phishing Attacks,” September 24, 2026.
Continue Exploring
COOP Keeps Government Operating. But What Keeps Its Information Continuous?
AI Needs Freedom. Freedom Needs a Constitution.